Plugin4Shell: Zero Click Flaw Lets Attackers Swap Trusted Plugins in Four AI Coding Agents
A newly disclosed flaw called Plugin4Shell affects four of the most popular AI coding agents: Claude Code, OpenAI Codex, GitHub Copilot and Gemini CLI. Security startup AIR published the details on September 17, 2026. The flaw lets an attacker who controls a plugin's code repository run their own code on a developer's machine without a single click. Anthropic and OpenAI have shipped fixes, but Copilot has no patch and Google will not fix Gemini CLI.
What is Plugin4Shell?
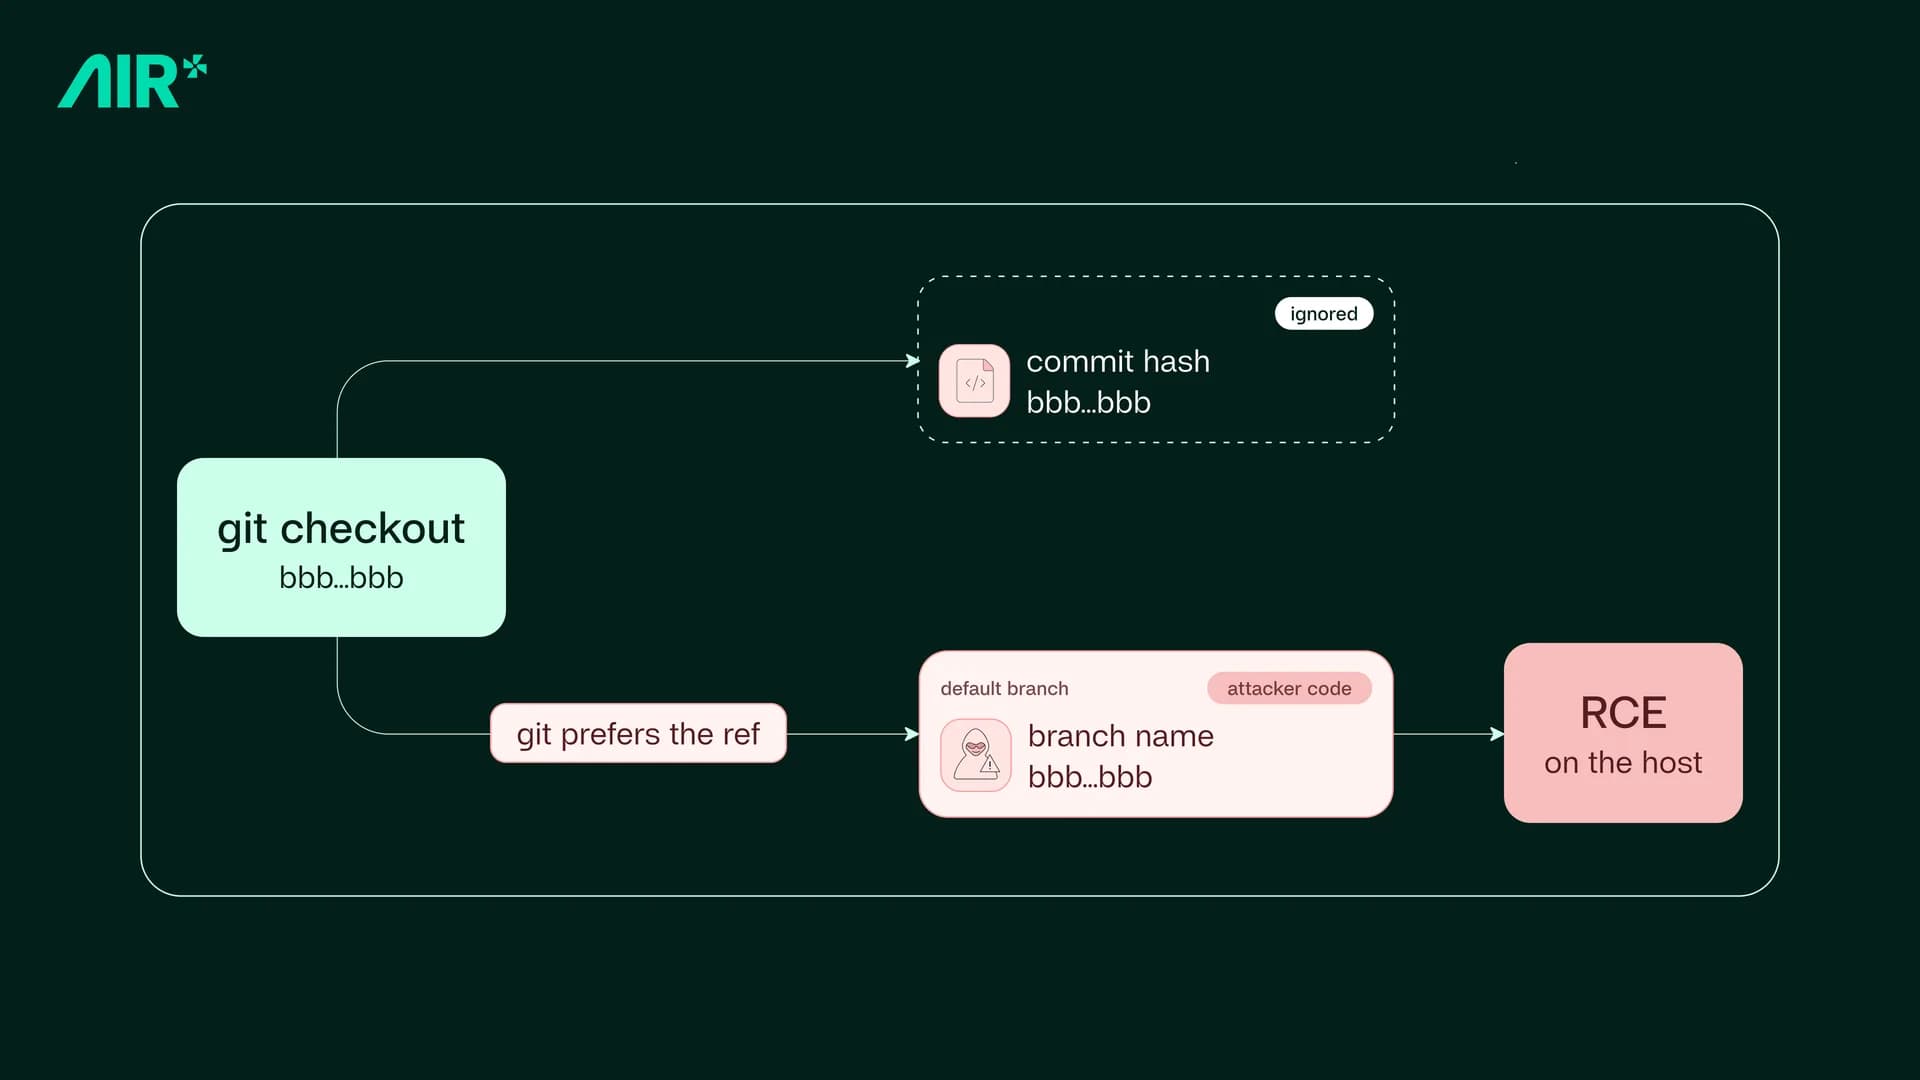
Plugin4Shell is a weakness in how AI coding agents install plugins from marketplaces. A marketplace locks each plugin to one reviewed version using a SHA pin, a long code that points to an exact commit. AIR found that the agents download that version but never confirm the code they received is really that commit. So anyone who controls the plugin's repository can swap in malicious code while the pin still looks fine. Since plugins often run with the developer's own access, the damage can reach source code, cloud keys and internal systems.
How the attack works
In Claude Code, Codex and Copilot, the attacker creates a branch named exactly like the pinned commit and makes it the default branch. Git prefers a branch over a commit with the same name, so the agent ends up with the attacker's code. Gemini CLI is fooled in a slightly different way, with the same result.
It works without any click because Claude Code and Codex update plugins in the background by default. Even an already installed plugin can be replaced silently.
AIR describes two routes. An attacker can publish a genuine plugin, get it approved and change it later, or take over a popular plugin's repository. In earlier SkillJacking research, AIR found 925 hijacked skills reaching about 134,000 agents.
Who has fixed it and who has not
Claude Code: fixed in version 2.1.179.
Codex: fixed in version 0.146.0.
GitHub Copilot: no patch. A GitHub spokesperson told The Register that GitHub blocks branch and tag names resembling commit hashes, so the attack cannot work there. AIR says marketplaces on Bitbucket or self hosted servers can stay exposed.
Gemini CLI: Google deprecated the tool and will not patch it. It points users to Antigravity, which has no plugin SHA pinning to bypass.
What developers should do now
Claude Code and Codex users, including teams across India, should check their version and update today. Everyone should review which plugins and marketplaces their agent trusts. Companies using Copilot should limit plugin sources and watch plugin repositories for sudden branch changes or ownership transfers.
A reality check
No attacks using Plugin4Shell have been reported so far. The claim of millions of exposed agents is AIR's own estimate, and AIR sells protection for AI agents, so treat that number with care. Two vendors have already patched it, so the flaw is not just theory.
The bigger lesson
A SHA pin works like a lock, and a lock only helps if someone checks that it actually clicked shut. AIR says one extra check after checkout, comparing the real commit with the pinned one, is enough to close the gap.
Sources: AIR Security
Comments
- Be the first to comment.